Stop lateral movement across your hybrid, multi-cloud environment
Unified platform for visibility, policy, and enforcement — with or without an agent. Works across your data center, endpoints, containers, Azure, AWS, GCP, and OCI. No rip-and-replace, no new console.

Cloud adoption is universal. Cloud security isn't.
88% of organizations run production applications on public cloud infrastructure or platform services.
Of the top challenges organizations say they face or expect to face with cloud-native applications, security is the No. 1 concern.
Organizations with a mature Zero Trust strategy are 4.3 times more likely to report complete visibility into traffic across environments.

Why cloud native controls aren't enough
Visibility gaps, misconfigurations, and uncontrolled lateral movement leave your workloads exposed.
Cloud-native controls weren't built to cover east-west traffic - the workload-to-workload movement inside your environment.

Cloud migrations carry data-center-era access straight into the cloud. Attackers, including automated and Al-driven threats, exploit that gap.
Each cloud provider has its own console, so there's no single policy view across Azure, AWS, GCP, and OCl. Fragmented visibility leads to blind spots and inconsistent rules.

The Illumio difference
A complete, real-time view of your hybrid multi-cloud — every workload, every connection, every risk.
See your cloud clearly
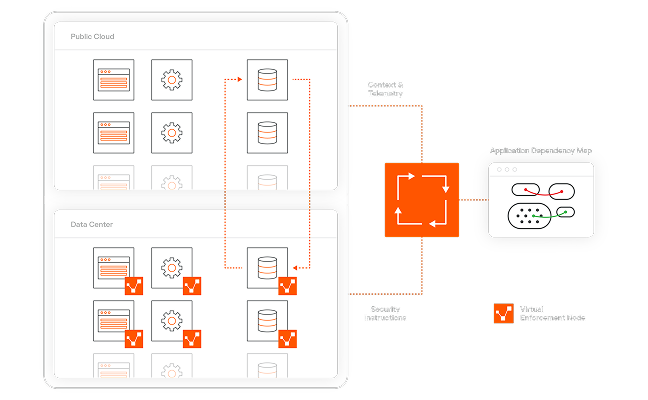
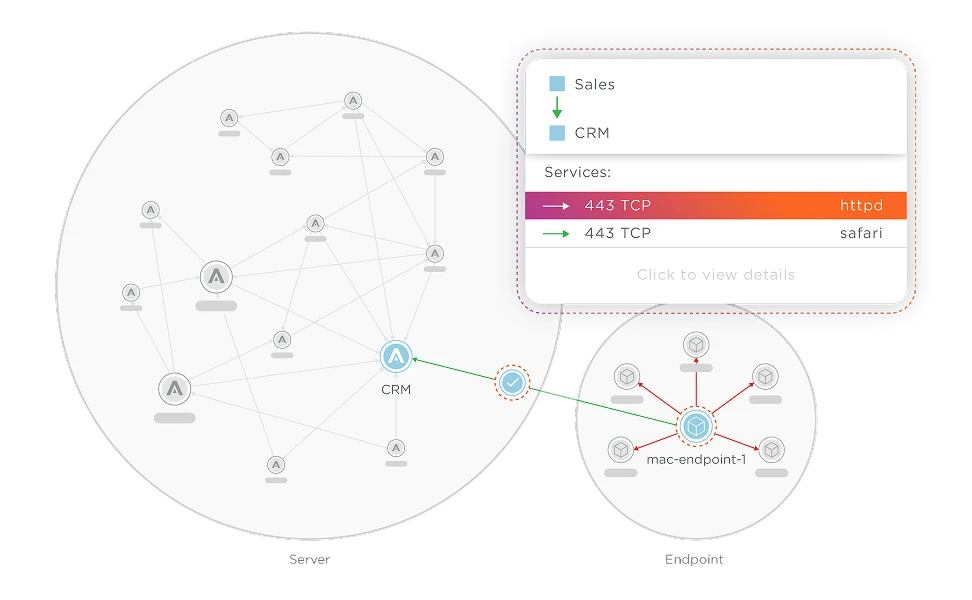
Illumio simplifies cloud sprawl, constant change, and complex interdependencies. Get a complete, real-time view of every workload. application, and dependency across hybrid and multi-cloud environments. See misconfigurations, hidden assets, and unprotected pathways — and block unwanted lateral movement.
Contain risk, not innovation
Agility shouldn’t come at the cost of security. Illumio turns cloud complexity into control by giving you deep observability and automatically enforcing segmentation and least-privilege policies that scale. When attackers try to move, their paths are cut off instantly — without disrupting workloads or slowing down deployment.

Why organizations choose Illumio for cloud security
One platform to see it all, control it all, and contain breaches fast — across every cloud.
One console for east-west visibility and policy across Azure, AWS, GCP, OCl, and on-premises - not a separate tool and rule set per cloud.
A real-time map of every workload and dependency across your hybrid multi-cloud - so threats surface and get contained fast.
Label-based policy follows the workload through auto-scaling, redeployment, and IP changes - no manual rule updates.
Draft-view shows exactly which connections a rule would change before it goes live, so you're not risking an outage to close a gap.
As the first breach containment platform, Illumio isolates compromised systems instantly to stop lateral movement before it spreads.
As your environment grows, Illumio grows with you - providing unified visibility, control, and resilience across every cloud and workload.
Cloud east-west security: common questions
Straight answers on segmenting east-west traffic across AWS, Azure, GCP, and OCI.

Most cloud teams don't know how exposed their east-west traffic is until they map it.
Illumio builds that map in minutes.
Illumio Collaborates with Microsoft to Strengthen Company's Cyber Resilience and Prevent Breaches at Scale

Illumio Segmentation for Cloud
Get integrated visibility and breach containment for hybrid, multi-cloud applications and workloads with Illumio Segmentation for cloud.

The Cloud Resilience Playbook
Learn how to combat, contain, and conquer breaches in the cloud with microsegmentation.

Illumio Segmentation for Containers
Strengthen container security with Illumio Segmentation by gaining visibility, enforcing consistent policies, and containing lateral movement across hybrid cloud environments.